


Trusted by companies you know and love


The Risk & Compliance Team Challenge
Every check is manual and every gap invisible until audit.
Your team owns third-party governance, but the due diligence lives in spreadsheets.
Certificates expire without anyone noticing, risk assessments go stale between reviews, and one unscreened vendor lands on your desk.
The problem is the gap between what governance requires and what your tools can prove.
How Gatekeeper Helps
Go from chasing evidence to proving governance.
Trade raw submissions
for scored results.
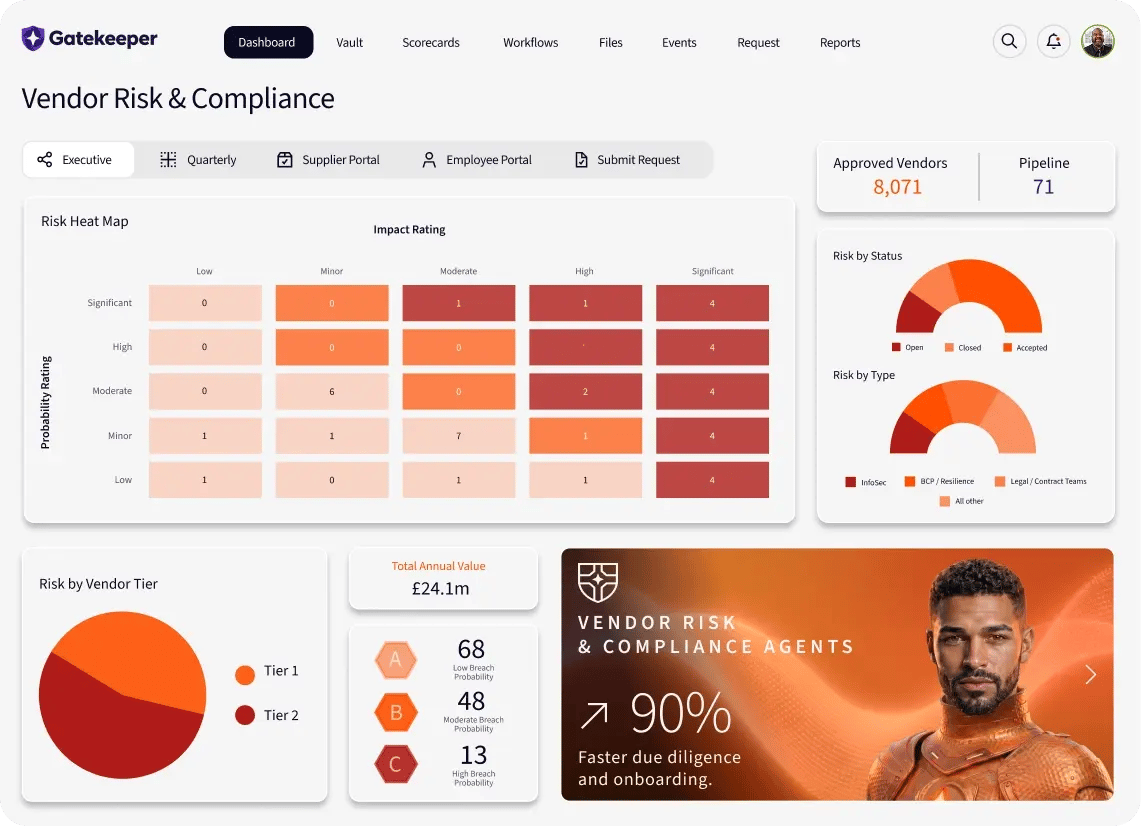
Business teams request a new vendor through a portal. Vendors complete your questionnaires, upload their certificates, and we screen them for financial health, sanctions, and adverse media through our data partners.
Instead of raw submissions, your team reviews scored results.
Automatic risk ratings.
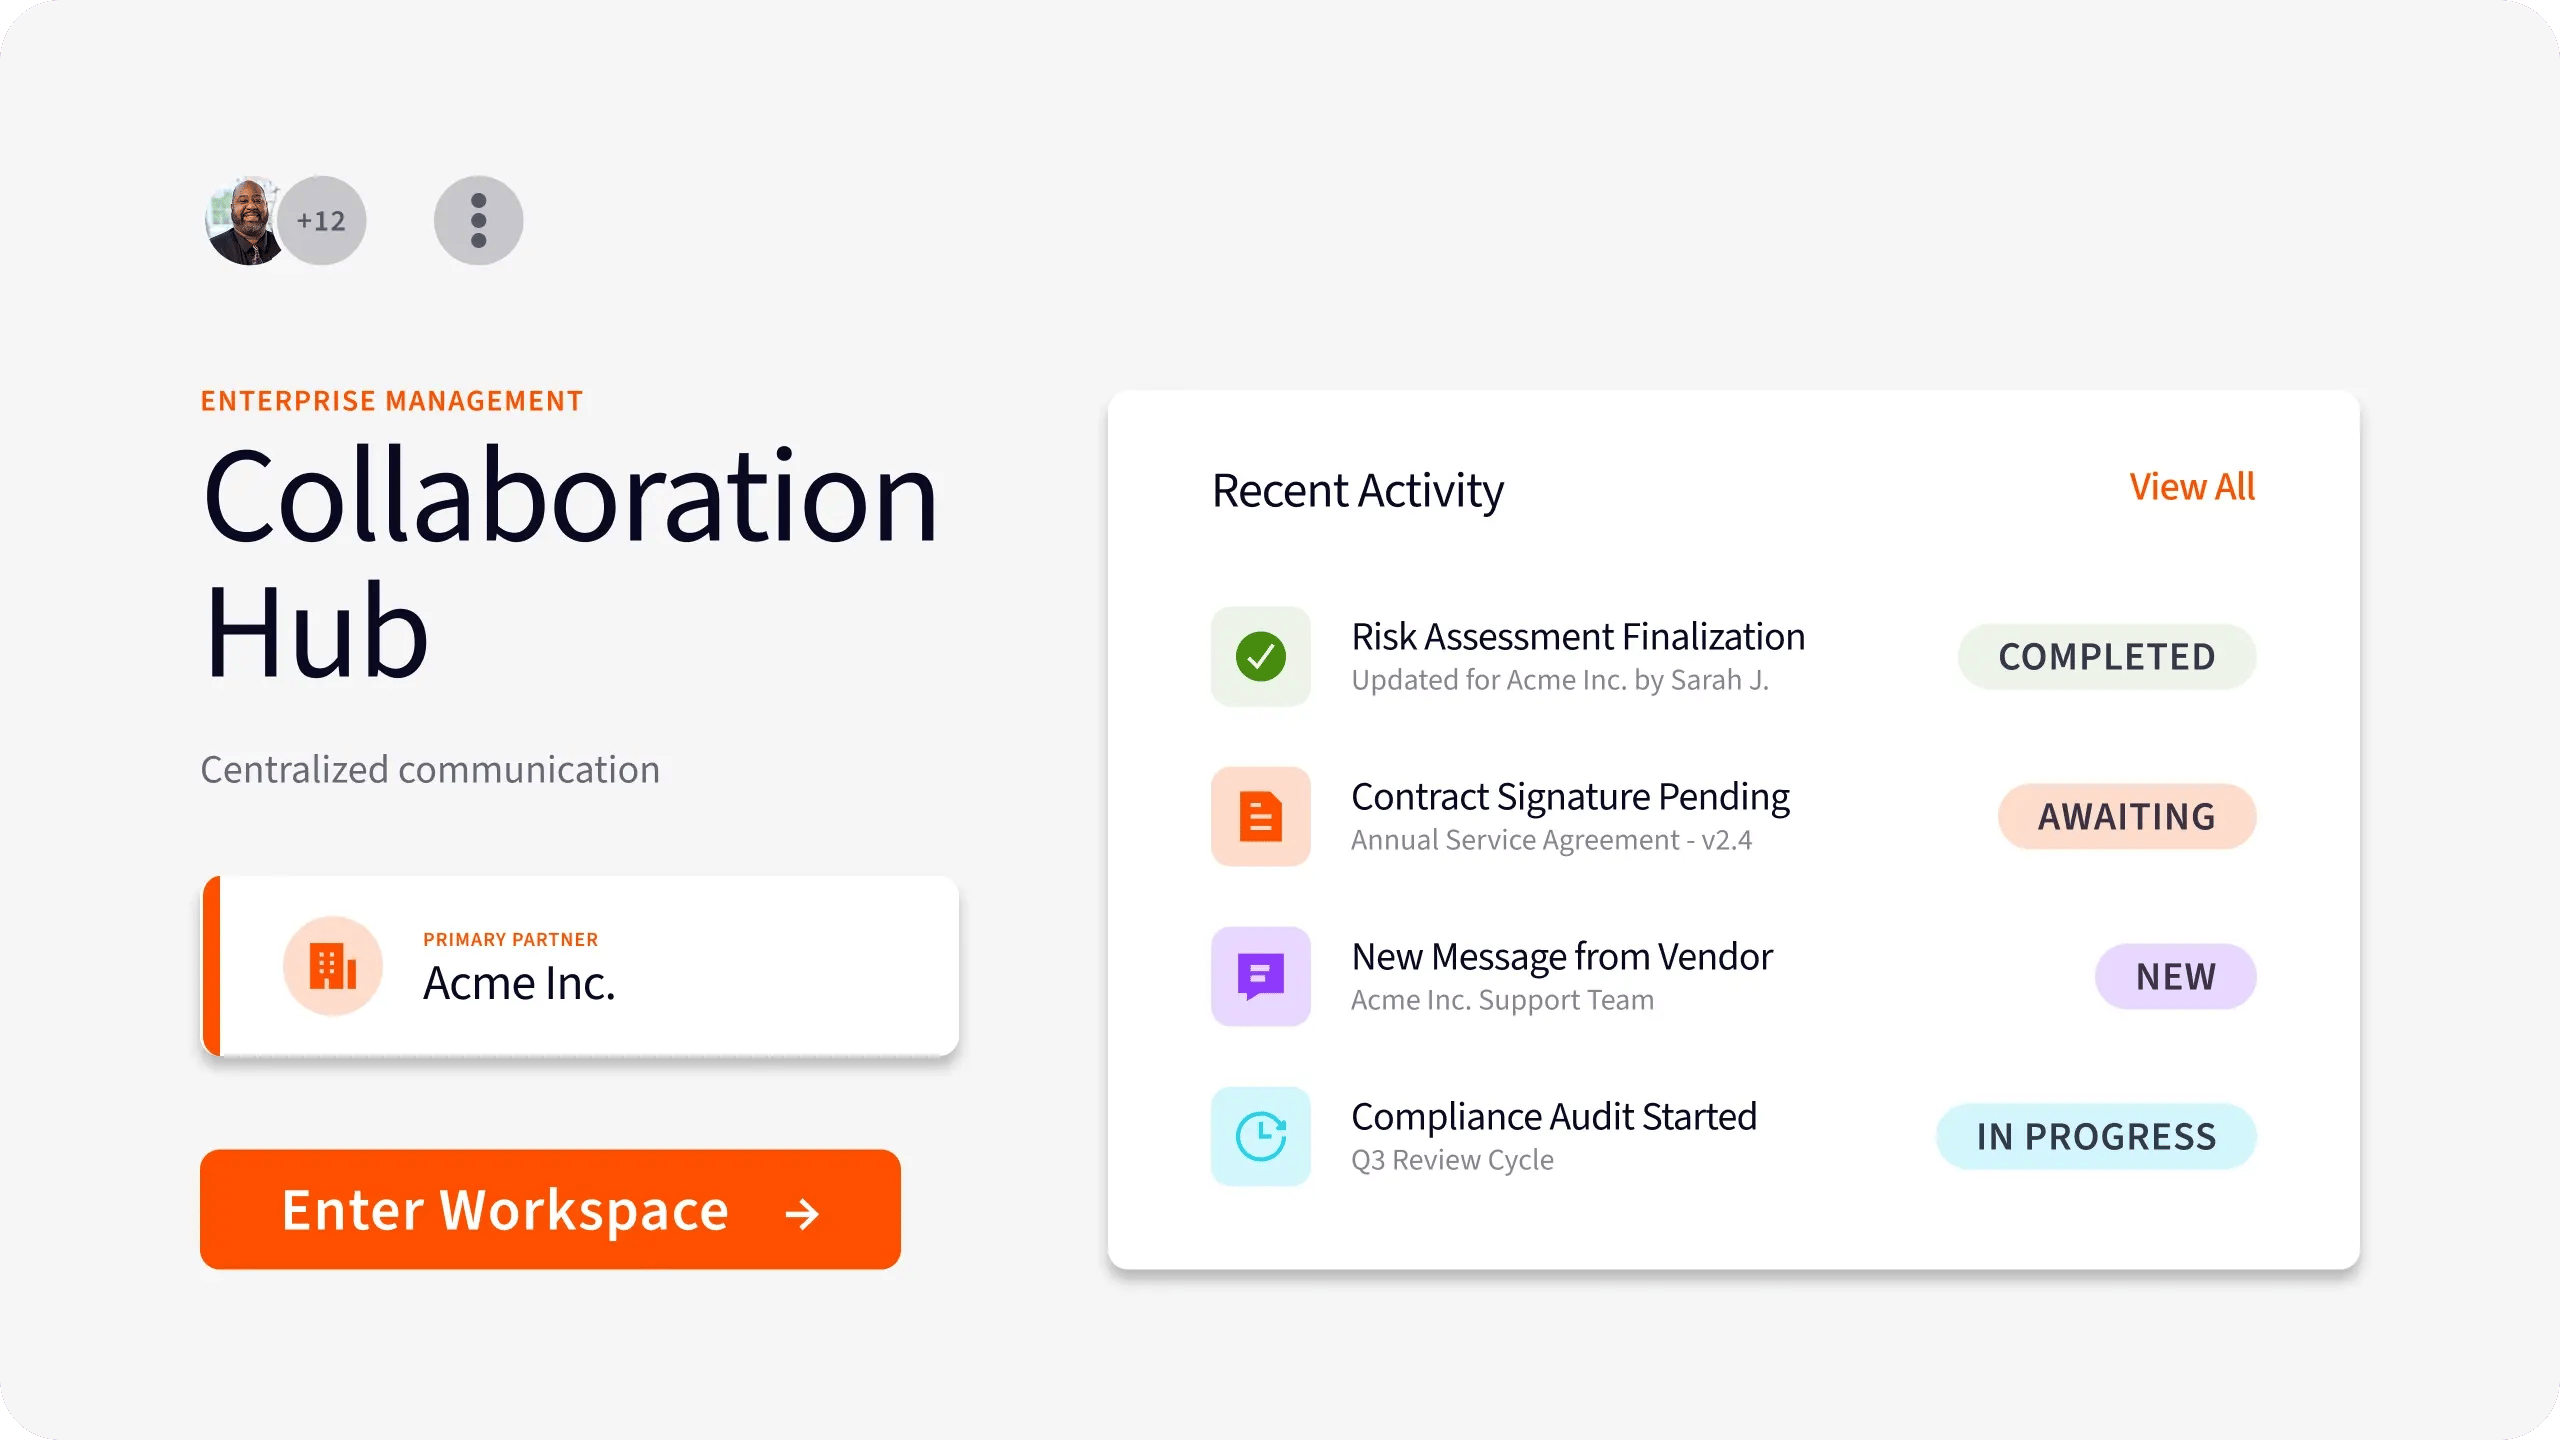
Your due diligence questionnaires are built into Gatekeeper with weighted scoring. When a vendor submits their answers, the platform automatically rolls the responses up into a risk rating.
ESG, modern slavery, privacy, cyber, financial viability: it all feeds into one score on one record.
Decisions made
on six-month-old data.
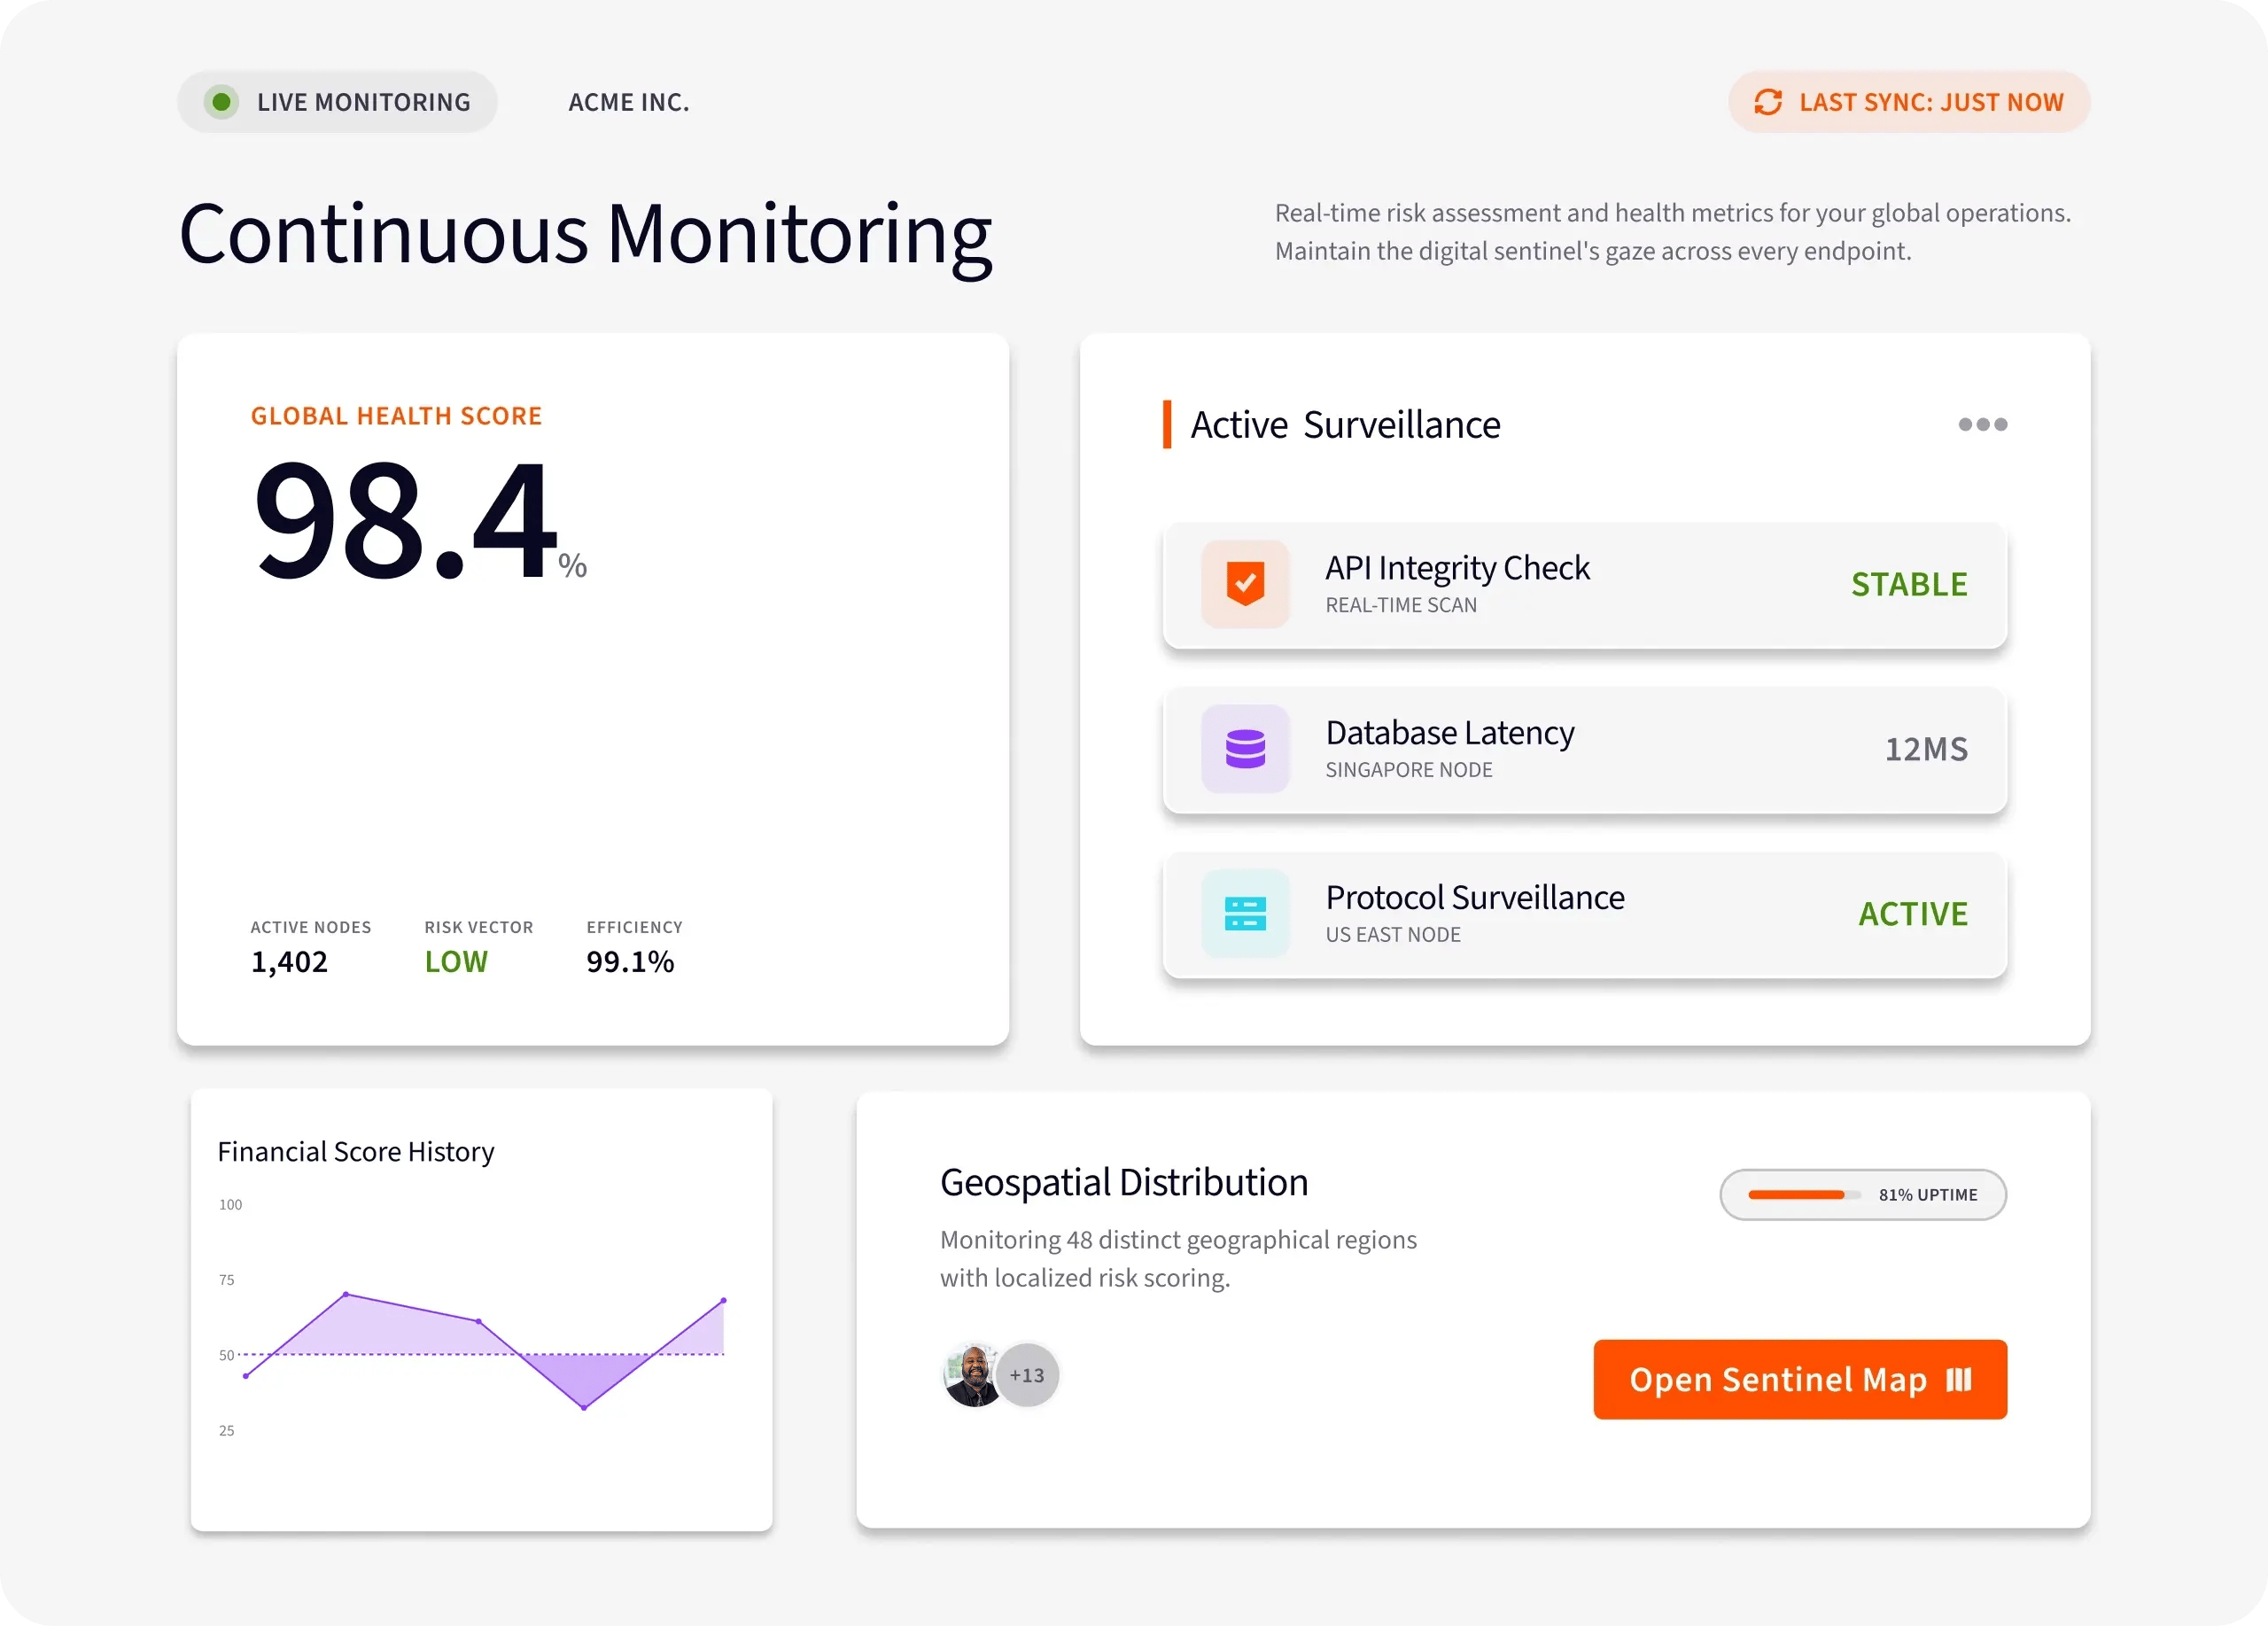
This is where most tools stop, but not Gatekeeper. Certificates, SOC reports and compliance attestations are tracked against expiry dates.
When a document is approaching expiry, the vendor is prompted to submit a renewal through their portal. If they don't respond, it escalates.
Three teams, three systems,
one deadline.
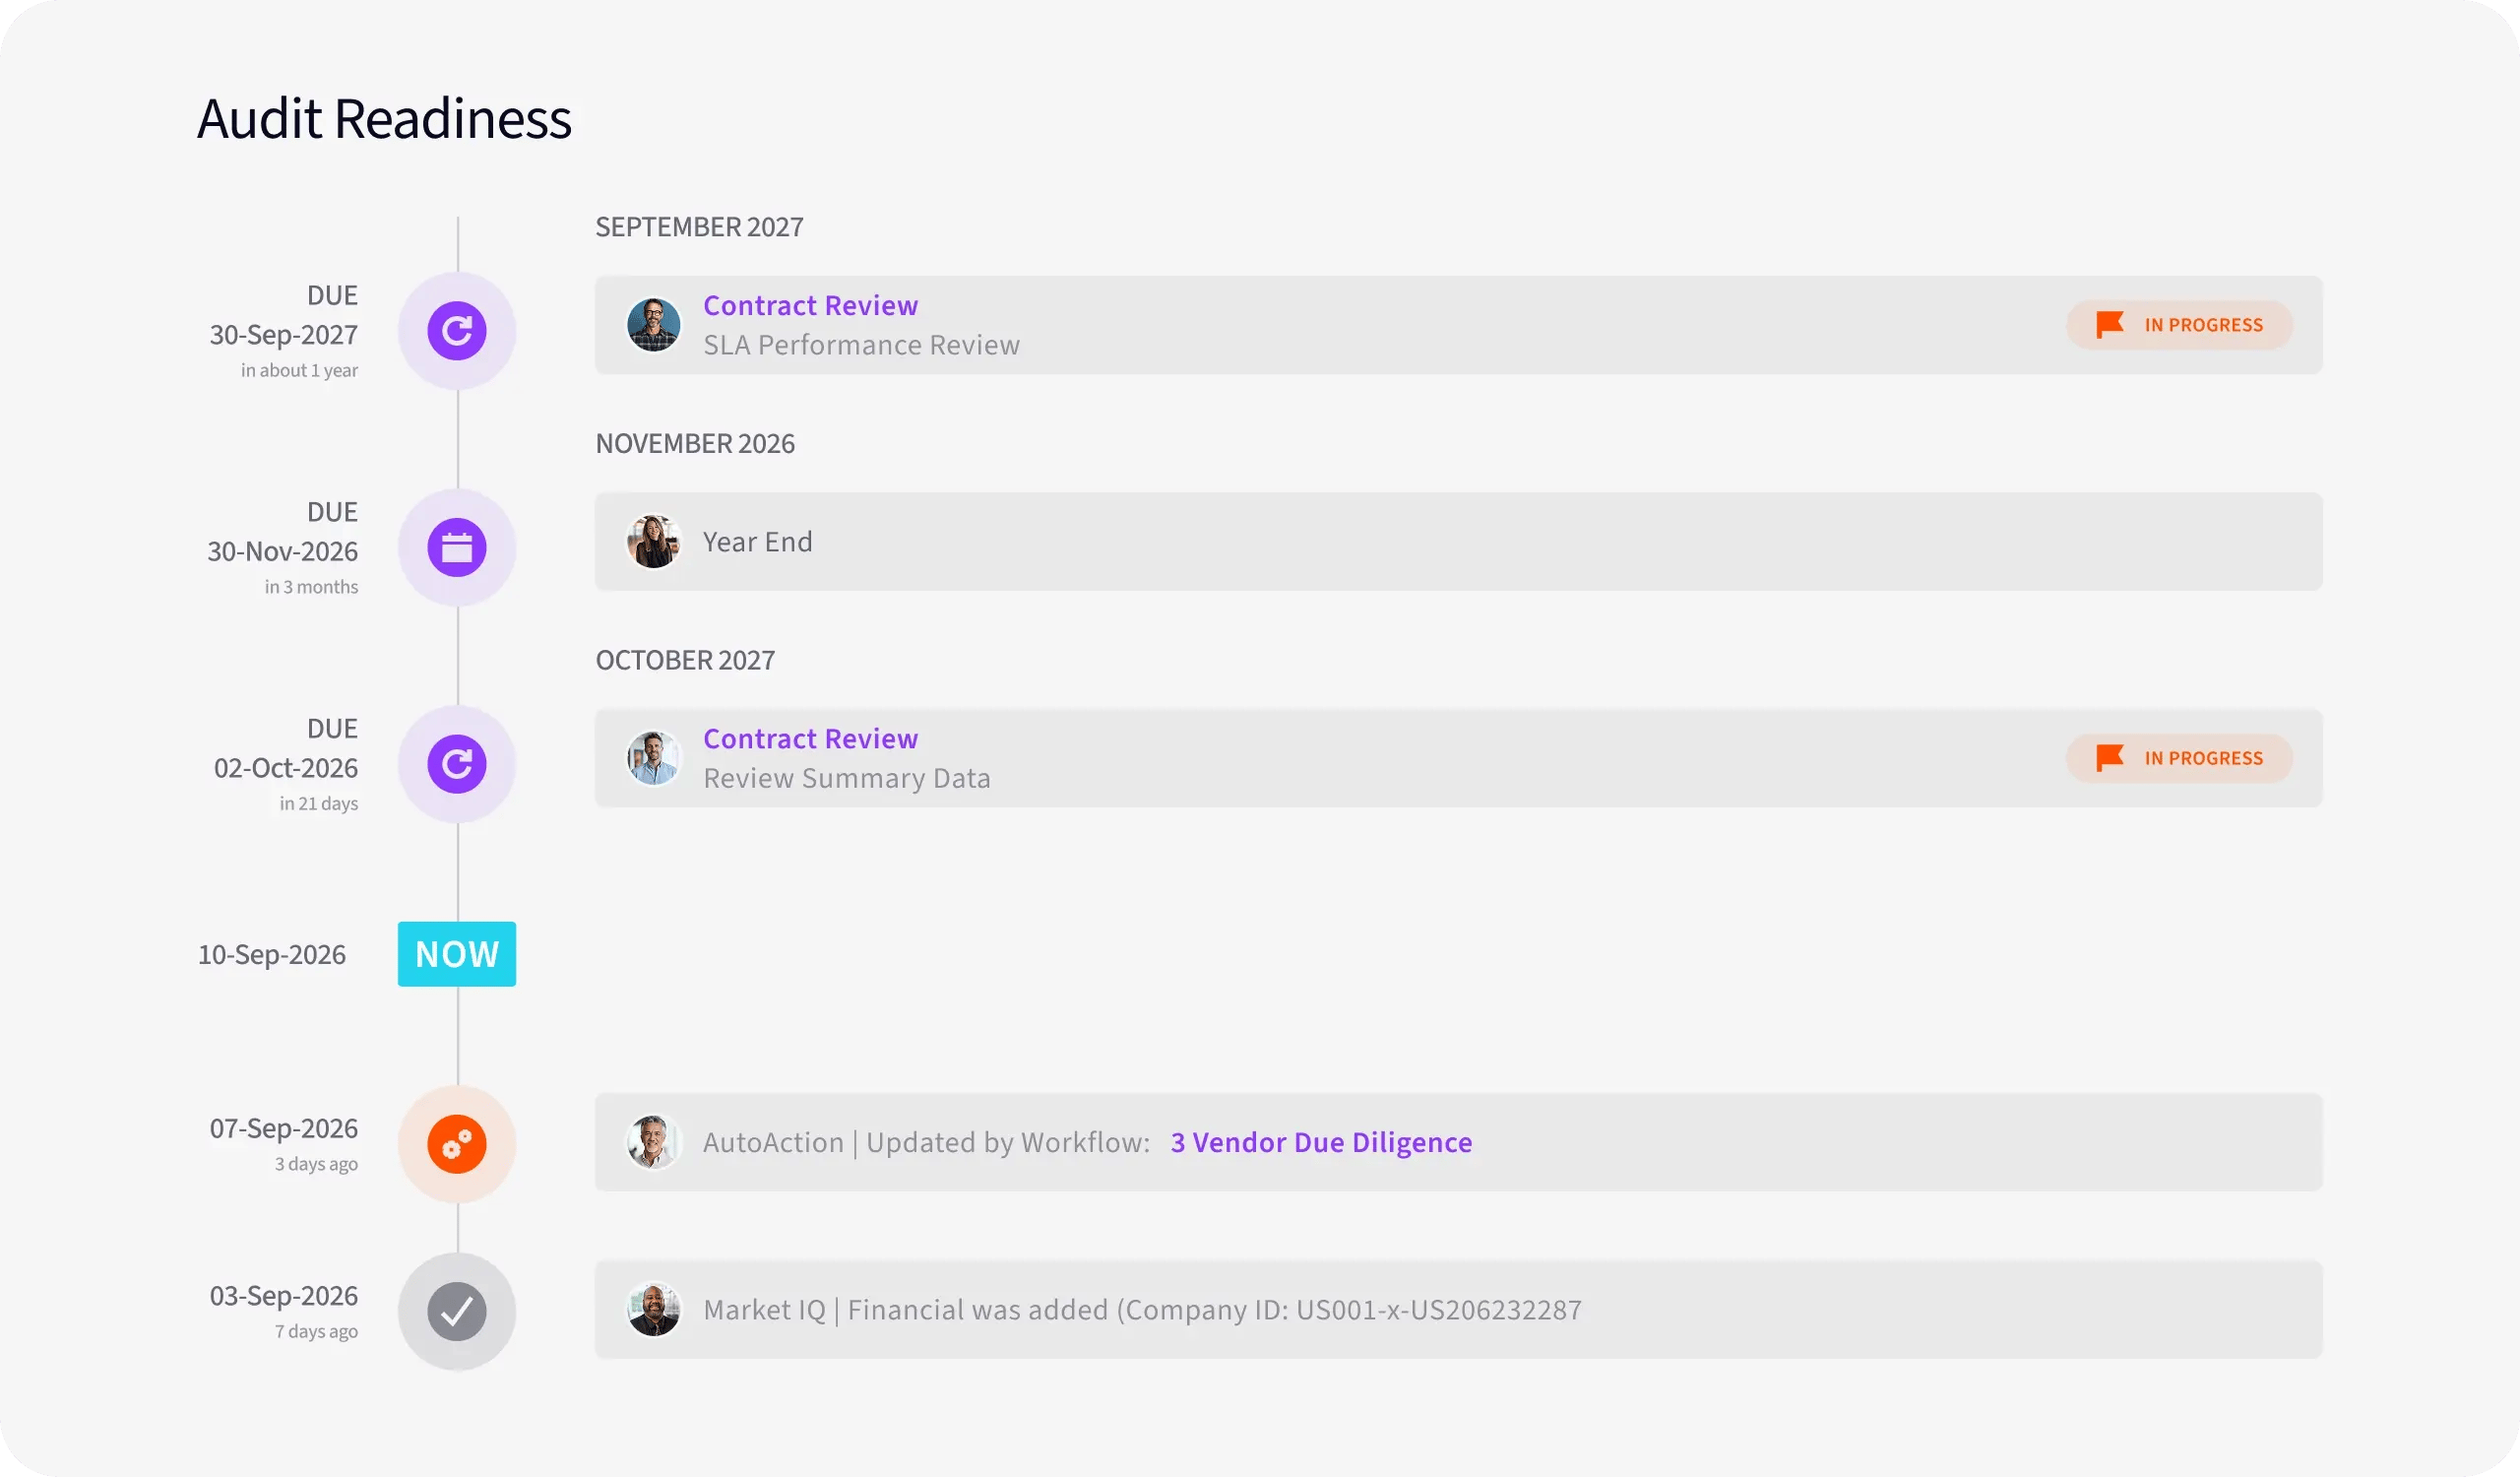
Every screening, questionnaire, approval and certificate renewal is recorded against the vendor record with a timestamp and an owner. The evidence trail is complete before the auditor asks.
Whether it is FCA, APRA CPS 230, DORA, SOC 2, or your own governance framework, the process is documented, and the trail is there. Your team presents the system, and the system presents the proof.
Gatekeeper Agents
that collect the evidence for you.
Agents extract contract metadata, flag clause deviations, apply redlines, chase missing information and monitor obligations after signature. Your team makes the decisions; Gatekeeper agents do the rest.
Recognised by customers
Case studies
Real teams, real results.
-
 How Funding Circle saved a total value of circa £1Million with Gatekeeper
case study
“Gatekeeper gives us excellent control and visibility of spend: we've been able to terminate contracts that no longer serve us with a total value of c. $1.3m.”
Krupa Patel,
Global Head of Procurement, Funding Circle
Explore Funding Circle
-
 How CompSource Mutual cut executive review time by 95% and freed 20 weeks of capacity.
case study
“There are a ton of companies out there making a lot of claims about AI. We've been blown away by what Gatekeeper's Agents can further improve.”
Tim Harvey
Procurement Director, CompSource Mutual Insurance
Explore CompSource Mutual
-
 How Inchcape Shipping Services Standardised International Vendor Management Processes
Case study
“The software is user-friendly, the implementation was seamless and the after-sales service is exceptional.”
Michael Adams
General Manager Global Strategic Sourcing
Explore Inchcape
Expert insight & opinion
Related guides & resources.
Explore our insights, opinions, and product information on vendor & contract lifecycle management
-
 Research
Beyond CLM: Hackett Group Research
Independent research on what changes when contracts connect to vendor risk and spend. For compliance teams being asked to prove governance across the full vendor lifecycle, not just at the point of signature.
Get the research
-
 Guide
The Executive Guide to AI Risk Management
How to close the AI governance gap: embedding AI risk controls across onboarding, contracting, reviews and renewals, and what regulators now expect under the EU AI Act, GDPR and ISO 42001.
Access the guide
-
Guide
A Guide to Vendor Lifecycle Management
Five chapters on managing vendors, contracts and third-party risk as one process, with actionable checklists and an ROI calculator.
Download the eBook